http://www.android4devs.com/
https://www.google.co.in/search?biw=1440&bih=739&q=android+facebook+graph+api+tutorial
http://www.easyfacebookandroidsdk.com/
https://www.google.co.in/search?biw=1440&bih=739&q=facebook+graph+api+tutorial+python
-----------------------------
http://quickblox.com/developers/SimpleSample-content-android#Add_Content_Management_System_.28CMS.29_to_your_application
---------------
https://github.com/mendhak/gpslogger GPS
HACKING
http://www.fromdev.com/2014/09/free-hacking-tools-hacker.html
HACKING TUTORIAL
http://www.wonderhowto.com/
https://www.google.co.in/search?q=how+to+use+ophcrack+for+windows+7
https://www.google.co.in/search?q=how+to+use+aircrack+ng+on+windows+8
Password Cracker Software
A
password cracker software, which is often referred to as a password
recovery tool, can be used to crack or recover the password either by
removing the original password, after bypassing the data encryption, or
by outright discovery of the password. In the process of password
cracking, a very common methodology used to crack the user password is
to repeatedly make guesses for the probable password and perhaps finally
hitting on the correct one. It cannot be denied that whenever we are
referring to cyber security, passwords are the most vulnerable security
links. On the other hand if the password is too completed, the user
might forget it. Password Cracker software are often used by the
hackers to crack the password and access a system to manipulate it.
In the next section you would be getting familiar with some of the
popular Password Cracker tools which are used by hackers for password
cracking.
It
is a free password cracker software which is based on the effective
implementation of the rainbow tables. It runs on a number of Operating
Systems like Mac OS X, Unix/Linux and Windows Operating System. It is
equipped with real-time graphs for analyzing the passwords and is an
open source software. Ophcrack has the capability to crack both NTLM
hashes as well as LM hashes.
Medusa
is one of the best online brute-force, speedy, parallel password
crackers which is available on the Internet. It has been designed by the
members of the website foofus.net. It is also widely used in
Penetration testing to ensure that the vulnerability of the system can
be exposed and appropriate security measures can be taken against
hacking.
Rainbow
Crack as the name suggests, is a cracker for hashes with the Rainbow
Tables. It runs on multiple operating systems such as Linux, Windows
Vista, Windows XP (Windows Operating Systems). It supports both
Graphical User Interface as well as Command line Interface. It's
software which is used for password cracking by generating rainbow
tables, fuzzing all the parameters.
Wfuzz
is a flexible tool for brute forcing Internet based applications. It
supports many features like Multithreading, Header brute forcing,
Recursion when discovering directories, Cookies, Proxy Support, hiding
results and encoding the URLs to name a few. Wfuzz is a useful tool for
finding unlinked resources like scripts, directories and servlets as
well.
Brutus
is one of the most flexible and free password crackers which operates
remotely. It is popular also because of its high speed and operates
under operating systems such as Windows 2000, Windows NT and Windows 9x.
Currently it does not operate under the UNIX operating system. Brutus
was initially designed to check network devices like routers for common
as well as default passwords.
L0phtCrack
which is now known as L0phtCrack6, is a tool which tests the strength
of a password given, as well as to recover lost passwords on Microsoft
Windows platform. Thus it is a tool for both password recovery as well
as auditing the password. It uses techniques such as Rainbow tables,
brute-force and dictionary to recover passwords.
Fgdump
is a powerful cracking tool. In fact, it's much more powerful than
pwdump6 as the latter has the tendency to hang whenever there is a
presence of an antivirus. Fgdump has the capability to handle this
problem of hanging by shutting down first. It later restarts the
Antivirus software. It supports multi threading which is very relevant
in the multitasking and multi-user environment.
Every
password security study has revealed that the biggest security
weaknesses are the passwords. THC Hydra is a tool for cracking logins
and it is flexible as it supports various protocols. It is very fast and
at the same time, new modules can be easily added. Hydra can run on
operating systems like Solaris 11, OSX, Windows and Linux.
John
the Ripper is a free software for password cracking which was
originally designed for the Unix Operating System. At present, it can
run on 15 Operating systems which includes 11 different versions of
UNIX, Win32, DOS and BeOS. It has the capability to combine several
password crackers into a single package which has made it one of the
most popular cracking tools for hackers.
It
is a network software suite used in 802.11 Wireless Local Area
Networks. It consists of tools such as a packet sniffer, detector and a
WEP. This tool runs on both Windows and Linux Operating systems. It can
work with any type of wireless network interface controller, provided
the driver is supporting the raw monitoring mode.
Cain
and Abel, often referred to as Cain, is a tool for recovering the
password in the Windows platform. It has the capability to recover
various kinds of passwords using techniques such as cracking the
password hashes by using brute-forcing, dictionary attacks,
cryptanalysis attacks and packet sniffing in the network.
The
objective of this security tool is to locate the valid user identities
in a Virtual Public Network along with the secret key combinations. Once
this is accomplished, this information can be used easily by a hacker
to have access to a VPN in an unauthorized manner
Wireless Hacking Tools
Wireless
Hacking Tools are those hacking tools which are used to hack into a
wireless network which is usually more susceptible to security threats.
One must also ensure that the network is completely secured against
hacking or other malwares. The list of wireless hacking tools which
would be discussed now can be used to do a Penetration Testing for a
Wireless Network. This is an intentional attack on a network to detect
security vulnerabilities by accessing its data and functionality.
It
is a software suit specially designed for a wireless network and which
operates under both the Windows and the Linux Operating System.
Aircrack-ng consists of a packet sniffer, WPA cracker and analysis tool
and a detector for the wireless Local Area Networks (802.11). The best
part of this software suit is one need not install it to use it. It is a
collection of files which can be easily used with a command prompt.
There have been many wireless hacking tools exposed in recent past. When
a hacker hacks a wireless network, it is supposed to defeat the
Wireless network’s security devices. The Wi-Fi networks i.e. the
Wireless LANs are more exposed to the security threats from a hacker
while compared to that of a wired network. While hackers are always
more than ready to hack specially if there are weaknesses in a computer
network, hacking is often a tedious and complicated procedure.
The latest code should have all you need to run aircrack-ng on windows.
But you may need to download the following files: cygwin1.dll, Peek.dll,
Peek5.sys and msvcr70.dll These you could get from anyone of the
following locations
dll-files. Also you can get the files here:
Unzip your download of aircrack-ng codes to
C:\aircrack-ng-[1x]. And then Download cygwin1.dll, Peek.dll, Peek5.sys
and msvcr70.dll from the links above; unzip and copy them to the folder
C:\aircrack-ng-[1x]\bin The aircrack-ng for windows install is done.
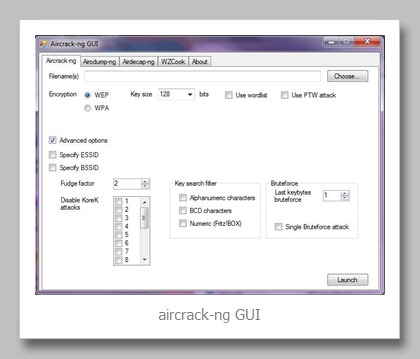
To run aircrack-ng Go to C:\aircrack-ng-[1x]\bin and double click on aircrack-ng GUI
Kismet
is a wireless detector system which detects possible intrusion to an
802.11 layer2 wireless network, it is also a sniffer. There are certain
plug-in supported by Kismet which enable sniffing media like DECT. . It
also has the capacity to infer whether a non beaconing network is
present or not via the data traffic in the network and a network is
identified by this tool by collecting data packets passively, detecting
hidden and standard named networks.
InSSIDer
is a network scanner which is used in a Wi-Fi network for the Windows
Operating System as well as the Apple OS X. It has been developed by
MetaGeek, LLC. It is used to collect information from both software and a
wireless card and is useful in selecting the availability of the best
wireless channel. It also shows those Wi-Fi network channels which
overlap with each other.
It
is a discovery tool for a wireless network for the Mac OS X operating
system. It has many features which are similar to another wireless
detector tool called Kismet. This tool is meant for expert network
security personnel and is not very user friendly for the beginners
In
order to log into a website, a user has submit details like his or her
username and password. The server validates these data and sends back a
“cookie”. The websites usually encrypts the password however does not
encrypt other details which leaves the cookie exposed to hacking threats
which are also known as HTTP session hijacking. Firesheep has a packet
sniffer which can intercept the cookies which are encrypted from Social
Media sites like Twitter and Facebook and comes with the Firefox web
browser. Firesheep is available for both the Windows and Mac OS X
operating system. It would also run on the Linux platform in the new
future.
It
is a powerful tool for packet injection in an 802.11 wireless network
and is very useful as it has the capability to send in forged
de-authentication packets. This feature is usually used by a hacker to
bring down a network.
KARMA
is an attack tool which takes the advantage of the probing techniques
that is used by used by a client of a WLAN. The station searches for a
Wireless LAN in the list of preferred network and it is then that it
makes the SSID open for an attacker who is listening. The disclosed SSID
is used by KARMA for impersonation of a valid WLAN and attracts the
station to the listening attacker.
NetStumbler
is a hacking tool which is used in the Windows Operating system and
comes with add ons which are used to hack a wireless network. It has the
capability to convert a WIFI enabled laptop on Windows OS into a
network detector in an 802.11 WLAN.
The
WebLab is a tool which teaches about the weaknesses of a WEP, how a WEP
works and how it is used to break a wireless network which is WEP
protected. It has the features of a WEP Security Analyzer.
Best Network Scanning & Hacking Tools
Nmap
or Network Mapper is a free open source utility tool for network
discovery and security auditing solution for you. It is a flexible,
powerful, portable and easy-to-use tool that is supported by most of the
operating systems like Linux, Windows, Solaris, Mac OS and others.
It
is an multi-functional application that is designed for scanning TPC
port. This is also a pinger and address resolver. It also has useful
features like ping, traceroute, WhoIs and HTTP request. There is no need
of installation as it is a portable application.
It
is a fast port and IP address scanner. It is a lightweight and
cross-platform application that has the capacity to scan the IP
addresses in any range and also in their ports. It simply pings each IP
address.
Packet Crafting To Exploit Firewall Weaknesses
Through Packet
crafting technique, an attacker capitalizes your firewall’s
vulnerabilities. Here are some packet crafting tools
Earlier
Hping was used as a security tool. Now it is used as a command-line
oriented TCP/IP packet analyzer or assembler. You can use this for
Firewall testing, advance port scanning, network testing by using
fragmentation, TOS and different other protocols.
It
is a powerful and interactive packet manipulation program. Scapy has
the capability to decode or forge the packets of a large number of
protocols at a time. One of the best feature is that it can confuse the
process of decoding and interpreting.
Netcat
is a simple Unix utility program. This program has the capability to
read and write data across network connections and it does so by using
UDP or TPC protocol. It was created as a reliable back-end tool.
Not
all the network protocols are powerful. In order to take advantage of
the weakness of certain network protocols Yersinia is created. It is a
full-proof framework that analyzes and tests the deployed networks and
systems.
It
is a command-line crafting and injecting utility tool used for network
packets. This program works for both Unix and Windows operating systems.
This is a well-suited tool for testing Network, Intrusion Detection
System, IP Stacks, Firewalls and many others
This
is again a command-line based utility tool. It has the capability to
establish a two bidirectional byte streams through which it transfers
data. In this tool streams can be constructed from a large set of
different data sinks.
Traffic Monitoring for Network Related Hacking
These tools allow users to monitor the websites one’s children or employees are viewing. Here’s a list of some of these tools
If
you want to convert your data into powerful insights Splunk tools are
the best options for you. The Splunk tools are the leading platforms for
operational intelligence. It can collect any type of data from any
machine in real time.
Nagios
is the name for the industry standard in monitoring IT infrastructure.
The Nagios tools helps you monitor your entire IT infrastructure and
have the capability to detect problems well ahead they occur. It can
also detect security breaches and share data availability with
stakeholders.
It
is versatile passive tool that is used for OS fingerprinting. This
passive tool works well in both Linux and Windows operating systems. It
has the capability to detect the hooking up of the remote system whether
it is Ethernet, DSL or OC3.
Ngrep
or network grep is a pcap-aware tool that allows you to extend
hexadecimal or regular expressions in order to match it against the data
loads of the packet. It can recognize IPv4/6, UDP, TCP, Ethernet, SLIP,
PPP, FDDI and many others.
Packet Sniffers To Analyze Traffic
These tools help capture and analyze incoming traffic on your website. Some of the popular ones are listed below
If
you want to put a security system, Wireshark is the must have security
tool. It monitors every single byte of the data that is transferred via
the network system. If you are a network administrator or penetration
tester this tool is a must have.
Tcpdump
is a command-line packet analyzer. After completing the designated task
of packet capturing Tcpdump will throw the report that will contain
numbers of captured packet and packets received by the filter. The user
can use flags like –v, -r and –w to run this packet analyzer tool.
It
is comprehensive suite in the middle of the attack. It has the feature
of sniffing the live connections and content filtering along with many
other interesting tricks. It offers three interfaces, traditional
command line, GUI and Ncurses.
Dsniff
is the collection of various tools that are used for penetration
testing and network auditing. The tools like dsniff, msgsnarf,
mailsnarf, webspy and urlsnarf passively monitor a network of
interesting data like files, emails, passwords and many others.
EtherApe
is graphical network monitor for UNIX model PCs after etherman. This
interactive tool graphically displays network activity. It features link
layer and TCP/IP modes. It supports Token Ring, FDDI, Ethernet, PPP,
SLIP, ISDN and other WLAN devices.
Web Proxies: Proxies fundamentally assist in adding encapsulation to
distributed systems. The client can request an item on your server by
contacting a proxy server.
It
is a Java-based HTTP/HTTPS proxy that helps in assessing the
vulnerability of web applications. It supports both viewing and editing
HTTP messages on-the-fly. It is supported by Unix and Windows systems.
There are some other features as well like client certificate, spiders,
proxy chaining and many others.
It
is free web debugging proxy tool that can be used for any browser,
platforms or systems. The key features of this tool include performance
testing, HTTP/HTTPS traffic recording, web session manipulation and
security testing.
A
passive and semi-automated application which is essentially a security
audit tool. It can accurately detect and annotate problems in web 2.0
platforms.
This
tool is the one that demonstrate HTTPS stripping attack. It has the
capability to hijack HTTP traffic on the network in a transparent
manner. It watches the HTTPS link and then redirect and maps those links
into homograph-similar or look-alike HTTP links.
Rootkit Detectors To Hack File System
This is a directory and file integrity checker. It checks the veracity of files and notifies the user if there’s an issue.
It
is a directory and file integrity checker that helps in creating a
database using the regular expression rules that it finds from the
config files. This tool also supports message digest algorithms and file
attributes like File type, Permissions, Inode, Uid, Gid and others.
Firewalls: Firewalls monitor and control network traffic. A firewall is
the quintessential security tool used by novices and tech experts
alike. Here are a few of the best ones for hackers:
Netfilter
offers softwares for the packet filtering framework that works within
the Linux 2.4.x and later series of kernel. The softwares of Netfilter
help in packet mangling including packet filtering along with network
address and port translation.
It
is an OpenBSD system that enables filtering of TCP/IP traffic and also
performs Network Address Translation. It also helps in conditioning and
normalizing of TCP/IP traffic along with packet prioritization and
bandwidth control.
Fuzzers To Search Vulnerabilities
Fuzzing is a term used by hackers for searching a computer system’s security vulnerabilities. Here is a list of a few:
It's
a reconnaissance web application security tool. Some of it's features
are dictionary-based probes and recursive crawls. A website's sitemap is
eventually annotated for security assessments.
This
tool is designed in such a way that it helps in brute-forcing web
applications. Wfuzz can be used for finding resources but it does not
play any role in finding the links like directories, servlets, scripts
and others. It has multiple injection points and allows multi-threading.
Wapiti
is a web application vulnerability scanner that allows you to audit the
security of the web applications that you are using. The scanning
process is “black-box” type and detects the vulnerabilities like file
disclosure, data injection, XSS injection and many others.
It
is a web application attack and audit framework that helps in auditing
any threat that the web application experiences. This framework is built
on Python and is easy-to-use and can be extended. It is licensed under
GPLv2.0.
Forensics
These tools are used for computer forensics,
especially to sniff out any trace of evidence existing in a particular
computer system. Here are some of the most popular.
It
is an open source digital intervention or forensic tool kit. It runs on
varied operating systems including Windows, Linux, OS X and many other
Unix systems. It can be used for analyzing disk images along with
in-depth analysis of file system like FAT, Ext3, HFS+, UFS and NTFS.
This
is a Linux based incident response system. It is also used in system
investigation and analysis along with data recovery and security
auditing. The most recent version of this tool is based on Ubuntu that
promises ease of use and stability.
It
is an open source forensic and intelligence application. It can be used
for gathering information in all phases of security related work. It
saves you time and money by performing the task on time in smarter way.
Encase
is the fastest and most comprehensive network forensic solution
available in the market. It is created following the global standard of
forensic investigation software. It has the capability of quickly
gathering data from wide variety of devices.
Debuggers To Hack Running Programs
These tools are utilized for reverse engineering binary files for writing exploits and analyzing malware.
GDB
is a GNU Project debugger. The unique feature of this debugger enables
the user to see what is happening inside one program while it is being
executed or check a program at the moment of crash.
It's
a powerful debugger for analyzing malware. It's unique features
include an advanced user interface with heap analysis tool and function
graphing.
Other Hacking Tools: Besides the aforementioned tools, there are myriad
of hacking tools used by hackers. They don’t belong to a particular
category, but are very popular among hackers nonetheless:
It
is a featured network utility tool. It has the capability to read and
write data across all network connections that uses TCP/IP protocol. It
is a reliable back-end tool that can be easily and directly driven by
other scripts and programs.
It
is a tracert or IP tracking tool that displays the path of internet
packets through which it traversed to reach the specific destination. It
identifies the IP address of each hop along the way it reaches the
destination.
It
is the tracing tool that helps the user to know the time that the data
packets took to reach the host. This is an online application where you
just need to place the host name or IP address and fetch the result.
It
is a complete searching and indexing system that is used for a domain
or internet. It works in both Linux and Windows system. It however does
not replace the internet-wide search systems like Google, Infoseek,
AltaVista and Lycos.
It
is a free and open source software command-line tool that transfers
data with URL syntax. It supports HTTP/HTTPS, Gopher, FTPS, LDAP, POP3
and many others. It can run under a wide variety of operating systems.
The recent stable version is v7.37.1.
Hacking Operating Systems
There are numerous professionals who aspire to have a career as
ethical hackers. Hacking is not an easy task as it requires great
insight about technology and programing. There are specific operating
systems as well that are specially designed for the hackers to use.
These operating systems have preloaded tools and technologies that
hackers can utilize to hack. This article offers a detailed overview of
various operating systems that are built keeping hacking in mind. All
these operating systems are unique from each other and have proved to be
a great resource for the hackers around the world.
This
operating system is built keeping the most savvy security personnel in
mind as audience. This is also a useful tool even for the early
newcomers in the information security field. It offers quick and easy
way to find and also update the largest database available for the
security tools collection till date.
This
is a creation of the makers of BackTrack. This is regarded as the most
versatile and advanced penetration testing distribution ever created.
The documentation of the software is built in an easy format to make it
the most user friendly. It is one of the must-have tools for ethical
hackers that is making a buzz in the market.
Security
Enhanced Linux or SELinux is an upstream repository that is used for
various userland tools and libraries. There are various capabilities
like policy compilation, policy management and policy development which
are incorporated in this utility tool along with SELinux services and
utilities. The user can get the software as a tested release or from the
development repository.
The
website of Knoppix offers a free open source live Linux CD. The CD and
DVD that is available contain the latest and recent updated Linux
software along with desktop environments. This is one of the best tools
for the beginners and includes programs like OpenOffice.org, Mozilla,
Konqueror, Apache, MySQL and PHP.
It
is a Linux distribution that is based on Ubuntu. If you want to perform
security assessment and penetration tests, this software is the one
that you should have in your repository. It proactively protects the IT
infrastructure. It has the capability to simplify the complexity of your
IT infrastructure with ease as well.
It
is security focused live CD that is created based on Gentoo. It has a
large number of customized tools and kernels including a hardened kernel
consisting of aufs patches. It can backport Wi-Fi stack from the latest
kernel release that is stable as well. There are development tools in
Pentoo that have Cuda/OPENCL cracking.
If
you are looking for a distro to be used in penetration testing and
cyber forensic investigation, then Matriux Krypton is the name that you
can trust. This is a Debian based GNU/Linux security distribution. It
has more than 340 powerful tools for penetration testing and forensics;
additionally, it contains custom kernel 3.9.4.
This
is regarded as the specialist tool that is specifically designed for
security auditing and penetration testing. It is a reliable, stable and
powerful tool to be used for this purpose and is based on the current
Ubuntu Linux distribution. It is a free and open source system that you
can download from the website.
It
is free and open source penetration testing distribution available over
the internet. It is based on Ubuntu 10.10, which is designed
specifically for the information security training students and
professional. It is fast and stable yet a powerful tool that works
perfectly for you. This software is a recommendation from most of the
users.
It
is free and open source penetration testing distribution available over
the internet. It is based on Ubuntu 10.10, which is designed
specifically for information security, training students and
professionals. It is fast and stable, yet a powerful tool that works
perfectly for you. This software is a recommendation from most of the
users.
It
is a live Linux environment that is designed in such a way that it
functions as a web-pen testing environment. The software CD contains
tools and programs that are open source and free. The tool selection is
based on the ones that the company themselves use for security of their
IT infrastructure.
It's
a great pentesting distro comprising of some innovative pentesting
tools. The software uses Fluxbox and is built using Debian Squeeze. One
of it's popular features is its ability to hack old Android based
systems.
It
is an Italian GNU/Linux live distribution list that was created as
project of Digital Forensic. It offers a complete forensic environment.
This environment is organized in such a way that it integrates the
existing software tools and software module, and finally throws the
result in the form of friendly graphical interface.
It
is one of the most stable and comprehensive distributions. It offers
stable and optimal functionalities with stable manger in real-time. It
is based upon 3.2 and 3.4 kernel Generic that is available in both 32
and 64 Bits. Bugtraq has a wide range of tools in various branches of
the kernel. The features of the distribution vary as per your desktop
environment
DEFT
is a distribution that is created for computer forensics. It can run in
live stream on the system without corrupting the device. The system is
based on GNU/Linux and the user can run this live using CD/DVD or USB
pendrive. DEFT is now paired with DART, which is a forensic system.
There
are various versions of Helix released by e-fense that are useful for
both home and business use. The Helix3 Enterprise is a cyber-security
solution offered by this organization that provides incident response.
It throws live response and acquires volatile data. Helix3 Pro is the
newest version in the block of Helix family products.
Encryption Tools
Times are changing and spying has become a common phenomenon
everywhere. There have been increasing instances where even the
governments have been found to be spying on their citizens from time to
time. This is one of the prime reasons why the importance of Encryption
has increased manifold. Encryption tools are very important because
they keep the data safe by encrypting it so that even if someone
accesses the data, they can’t get through the data unless they know how
to decrypt the data. These tools use algorithm schemes to encode the
data to prevent unauthorized access to the encrypted data.
Some of the popular Encryption Tools will be discussed in this article:-
TrueCrypt
is open source encryption tool which can encrypt a partition in the
Windows environment (except Windows 8); it’s equipped for creating a
virtual encrypted disk in a file. Moreover, it has the capability to
encrypt the complete storage device. TrueCrypt can run on different
operating systems like Linux, Microsoft Windows and OSX. TrueCrypt
stores the encryption keys in the RAM of the computer.
OpenSSH
is the short name for Open Secure Shell and is a free software suite
which is used to make your network connections secured. It uses the SSH
protocol to provide encrypted communication sessions in a computer
network. It was designed originally as an alternative to the Secure
Shell Software developed by SSH Communications Security. The tool was
designed as a part of the OpenBSD project.
It
an open source encryption tool available on both UNIX and Windows
operating system. It is a free implementation of SSH (Secure Shell) and
Telnet for both Windows as well as UNIX. The beauty of this tool is that
it supports many network protocols like Telnet, SCP, rlogin, SSH and
raw socket connection. The word PuTTY has no specific meaning, however
as in UNIX tradition, tty is a terminal name.
OpenSSL
is an open source encryption tool which implements the TLS and SSL
protocols. OpenSSL’s core library is written in the C programming
language. The fundamental cryptographic functions are implemented by it.
OpenSSL versions are available for operating systems like UNIX,
Solaris, Linux and Mac OS X. The project was undertaken in 1988 with the
objective of inventing free encryption tools for the programs being
used on the internet.
Tor
is a free encryption tool and has the capability to provide online
anonymity as well as censorship resistance. Internal traffic is directed
through a free network which consists of more than five thousand relays
so that the user’s actual location can be hidden. It is difficult to
track the Internet activities like visiting web sites and instant
messages; the most important goal of this tool is to ensure the personal
privacy of the users.
It
is an open source tool for the implementation of virtual private
network techniques so that secured site-to-site or point-to-point
connections using routers or bridges are possible, also remote access
is possible. OpenVPN offers the users a secured authentication process
by using secret keys which are pre-shared.
Stunnel
is a multi-platform open source tool which is used to ensure that both
the clients and the servers get secured encrypted connections. This
encryption software can operate on a number of operating system
platforms like Windows as well as all operating systems which are UNIX
like. Stunnel depends upon a distinct library like SSLeay or OpenSSL to
implement the protocols (SSL or TLS)
KeePass
is an open source as well as free password management tool for the
Microsoft Windows as well as unofficial ports for operating systems such
as iOS, Linux, Android, Mac OS X and Windows Phone. All the usernames,
passwords and all other fields are stored by KeePass in a secured
encrypted database. This database in turn is protected by a single
password.
Intrusion Detection System And The IDS Tools
An Intrusion
Detection System is a software application or a device which is equipped
to do network or system monitoring activities for any malicious threats
and sends reports to the management station. Intrusion detection tools
can help in identifying potential threats which can be dangerous for the
system or the network.
It
is an open source Network Intrusion System as well as a Network
Intrusion Prevention System which is free for all to use. It was created
in 1988 by Martin Roesch. It has the capability to perform packet
logging and analysis of real time traffic on networks which are using
the internet protocol.
NetCop
is an advanced intrusion detection system which is available
practically everywhere. NetCop makes use of a specific method to
classify the spyware. This is because there are several software
programs which intrude your privacy and which have different kind of
capabilities. NetCop gives a distinct threat level to each program, thus
classifying the threats.
Hacking Vulnerability Exploitation Tools
A tool which
identifies whether a remote host is vulnerable to a security attack and
tries to protect the host by providing a shell or other function
remotely, is called a Vulnerability Exploitation tool. Here is a list of
some o the popular ones:
Metasploit
was released in the year 2004 and it was an instant hit in the world of
computer security. Metasploit provides data on the vulnerabilities in
the security system and it helps in conducting penetration testing too.
It
is a penetration testing tool which is available as an open source. Its
goal is to automate the detection and exploitation process of the
injection flaws in SQL and to take over the database servers.
The
main objective of this tool is to access a vulnerable DB server; it's
used for pen testing so that the procedure of controlling a DB server
can be automated when the vulnerability of an SQL injection has been
tracked.
This
tool kit also known as SET, was designed by TrustedSec. The tool comes
as an open source code and is Python driven. It is used for conducting
Penetration Testing around Social Engineer.
It
is a web based security scanner which has an exploitation engine to
confirm the security vulnerabilities and makes the user concentrate on
elimination of security threats with its False-Positive free feature.
BeEF
is the short term for The Browser Exploitation Framework. It is a tool
for penetration testing which concentrates on a web browser and thus
accesses the actual security position of the environment it’s targeting.
Dradis
stands for Direction, Range and Distance. It is an open source
vulnerability scanner or application which provides the facility of
information sharing effectively, especially during assessing the
security of the system in a central repository.
Vulnerability Scanners
The scanners which assess the
vulnerability of a network or a computer to security attacks are known
as Vulnerability Scanners. The tools might function differently,
however all of them aim to provide an analysis on how vulnerable the
system or a network is. Here is a list of the best ones:
Nessus
is the world’s most popular vulnerable scanner topping the list in the
years 2000, 2003 and in the year 2006 survey on security tools. It's a
free to use vulnerability scanner for personal use in the non
enterprise environment.


